Grátis
Testes e segurança
code-review
Review a change against project standards and the originating specification using two review tracks.
322,4 milEstrelas27 milForks
Último push do repositório
Matt Pocock
Fluxos originais para sites, imagens, apresentações e tudo em movimento.
Review a change against project standards and the originating specification using two review tracks.
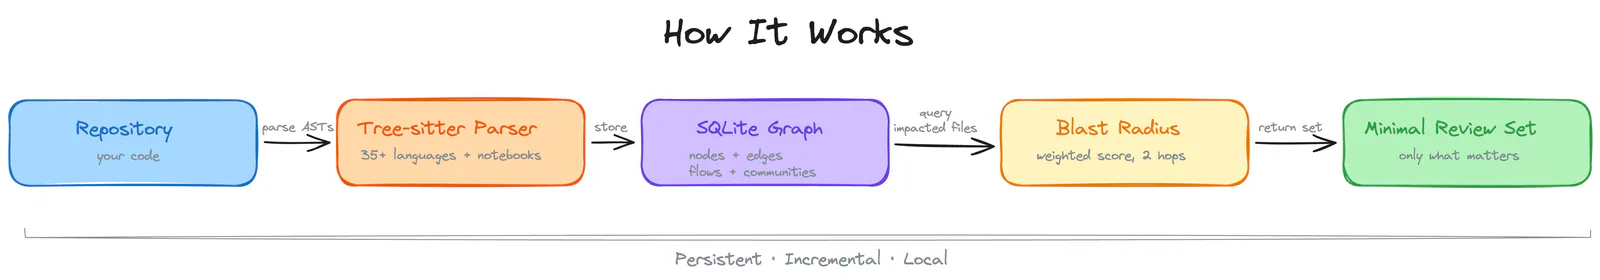
Review changes since the latest commit with incremental impact and blast radius analysis.
Review code changes using detected modifications and their effects on dependent code.
Build and incrementally update the dependency graph used by code-review-graph.
Review code for security, correctness, performance, maintainability and testing gaps.
Use a repository knowledge graph to locate relevant code and investigate reported issues.
Plan refactoring with dependency relationships and change impact analysis.

Review changes for correctness, readability, architecture, security and performance with actionable findings.
Graph-based code exploration, debugging, refactoring, and change review workflows.
Explore repository structure, symbols, and dependencies through the code review knowledge graph.
Evaluate code-review feedback against the actual code before accepting, clarifying or challenging it.
Review pull requests and branch diffs with graph context and a structured impact report.
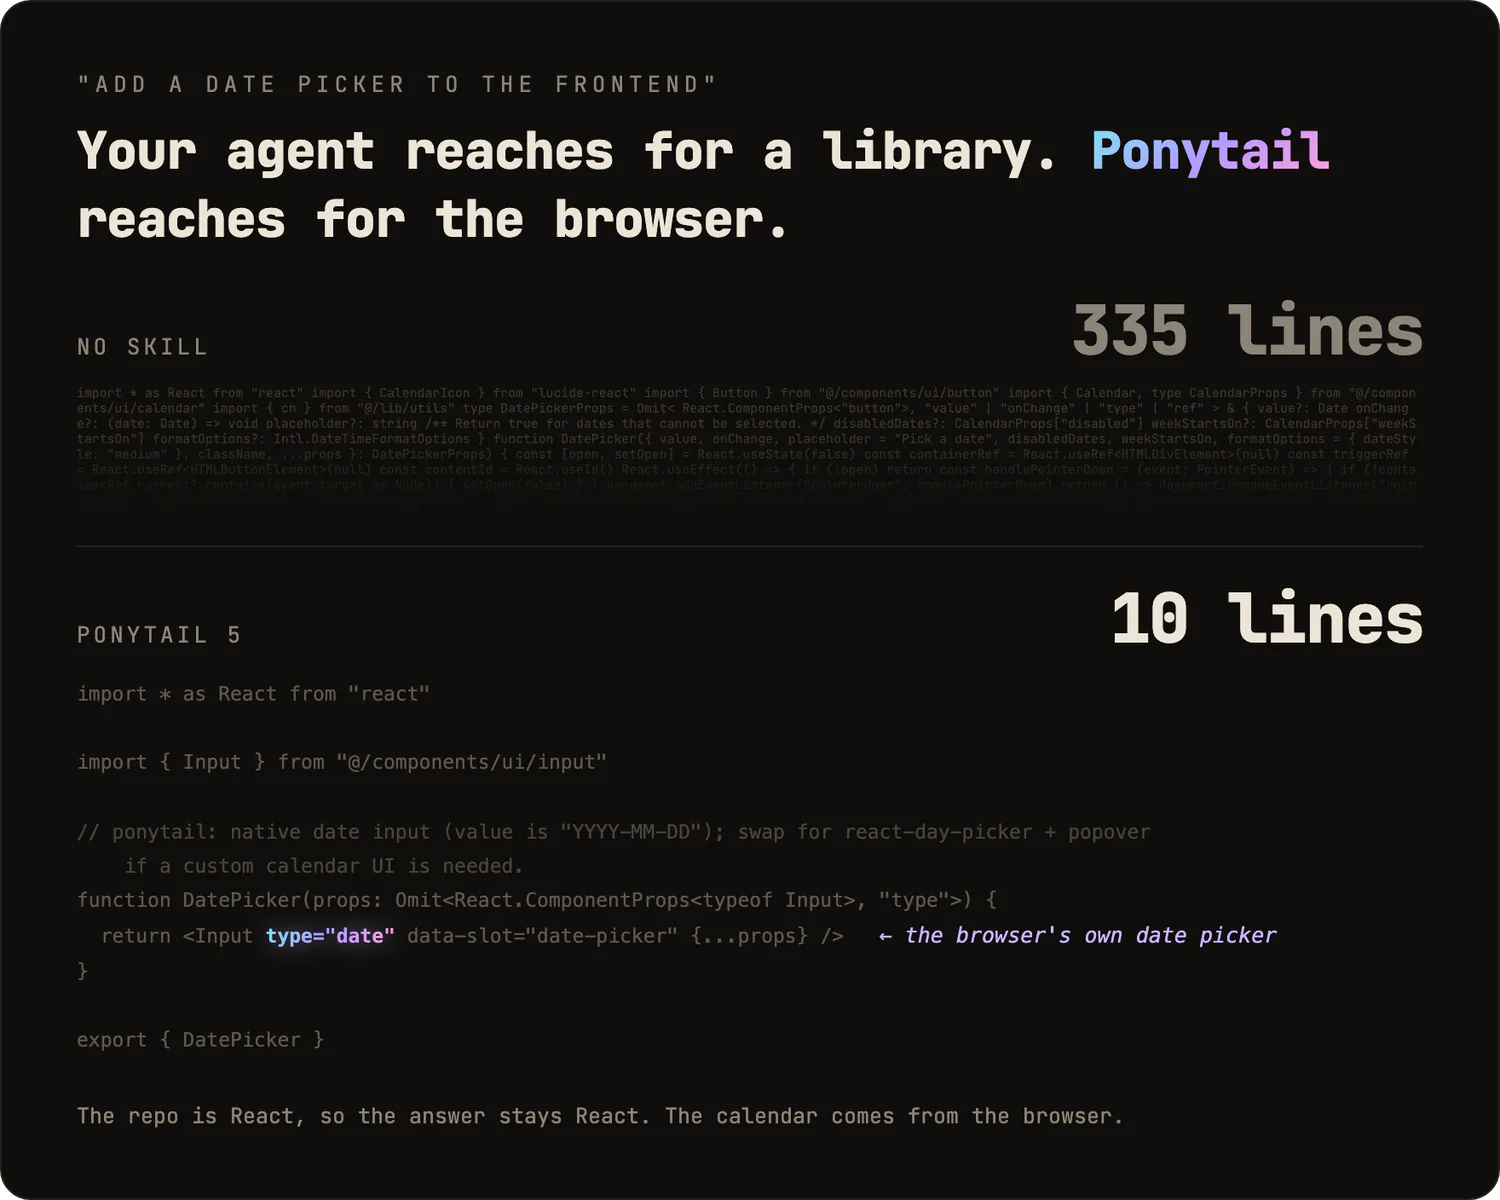
Review a change and its connected code for correctness, safety, performance and unnecessary complexity.
Performs AI-powered code review on Git changes using the `ocr` CLI from alibaba/open-code-review.
Delegation mode for open-code-review (OCR).
Review Git changes with the OCR CLI, using either a configured model provider or the host agent for review reasoning.
Scan React projects for correctness, accessibility, security, architecture and performance findings; triage and fix issues with the upstream workflow.
Review Renovate bot PRs that update GitHub Actions dependencies. Verifies supply chain integrity by checking pinned commit SHAs against upstream tagged releases, reviews changelogs for breaking changes, and confirms compatibility with existing workflow configurations.
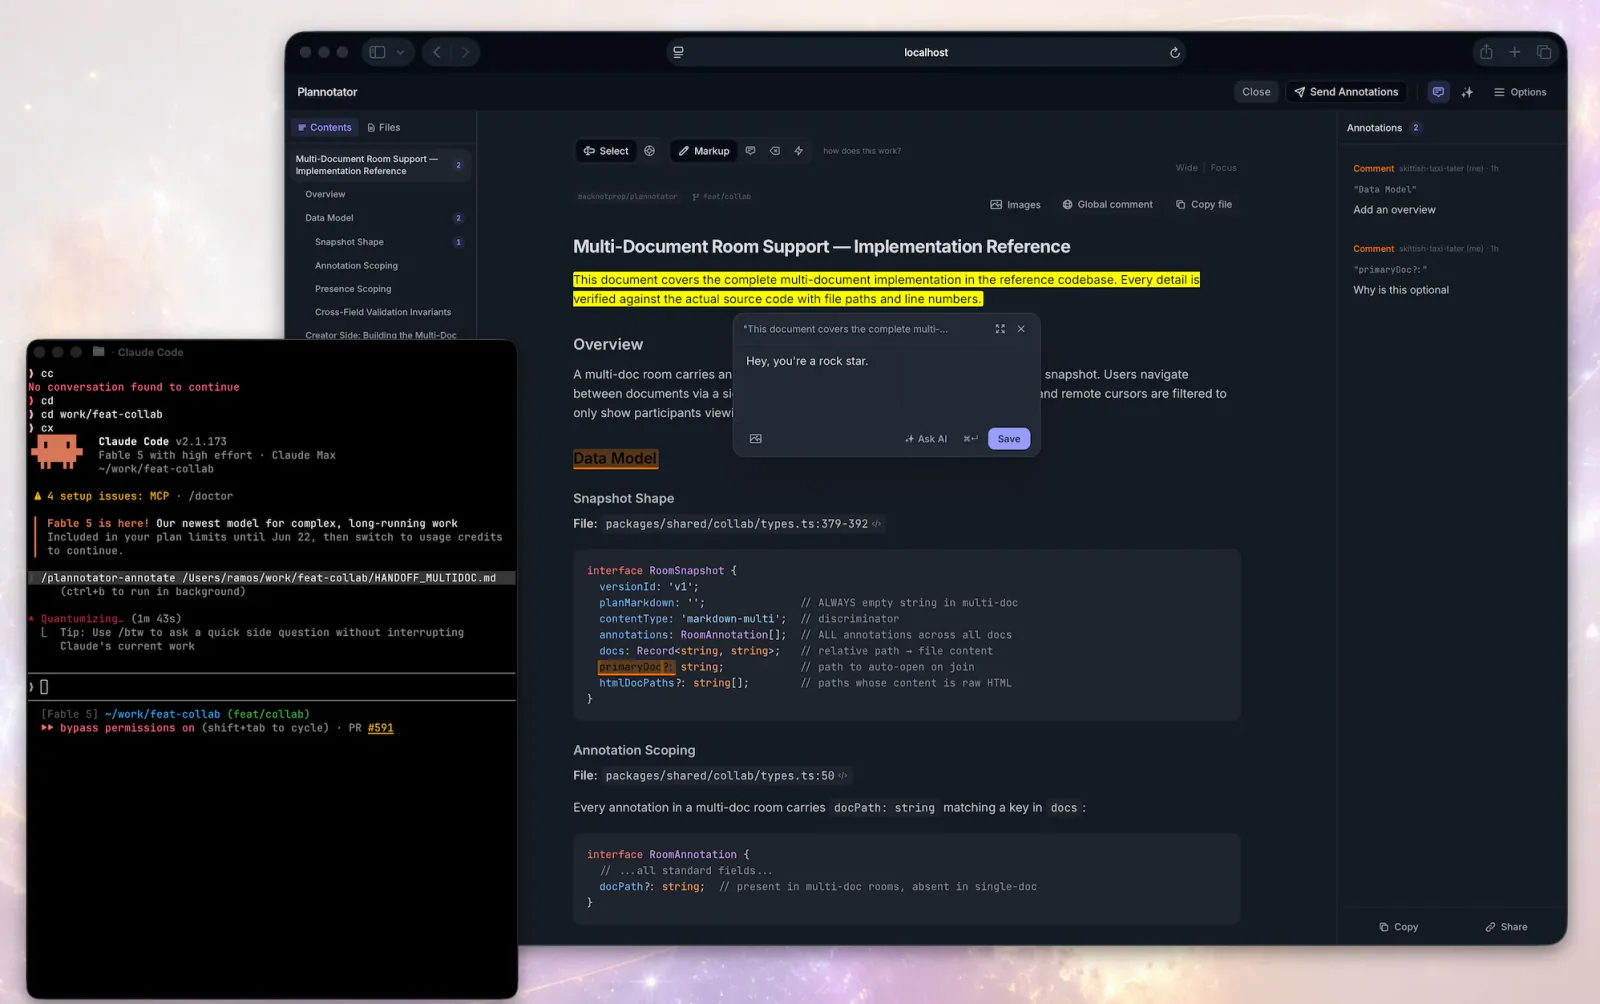
Organize and implement code-review feedback.
Read and triage existing pull request review comments, or address them when requested.
Explain Git diffs or pull requests, affected components and potential change risks.
Audit and update npm/Bun dependencies with supply chain integrity checks — verifies maintainers, publish age, tarball diffs, and provenance before bumping. Defers risky packages to ~/.supply-chain/notes/.
React Doctor workflows for scanning React code, planning fixes, inspecting Three.js and measuring runtime performance.
Search for existing JavaScript and TypeScript symbols before adding potentially duplicate code.