Open or update a pull request in this repository, including writing or rewriting its description.
7,6 milEstrelas359Forks
Último push do repositório
Fluxos originais para sites, imagens, apresentações e tudo em movimento.
Open or update a pull request in this repository, including writing or rewriting its description.
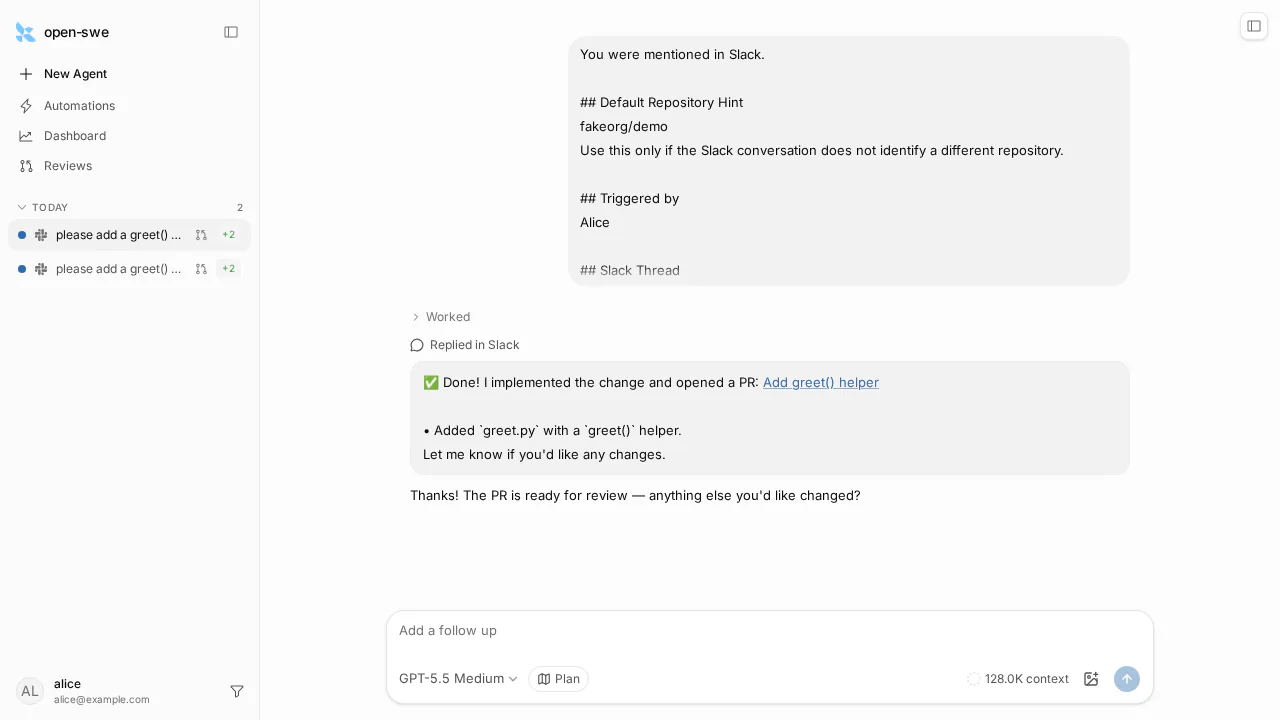
Write a pull request title and description using the project's preferred structure and change context.
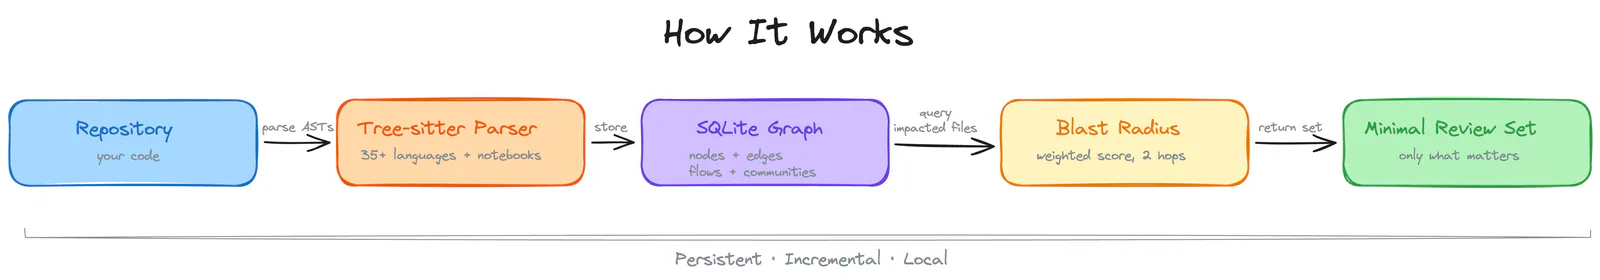
Review pull requests and branch diffs with graph context and a structured impact report.
Monitor a pull request until CI succeeds, investigate failures and retry only confirmed flaky workflow jobs.
Prepare a focused Tantivy pull request from staged changes with a generated commit message.
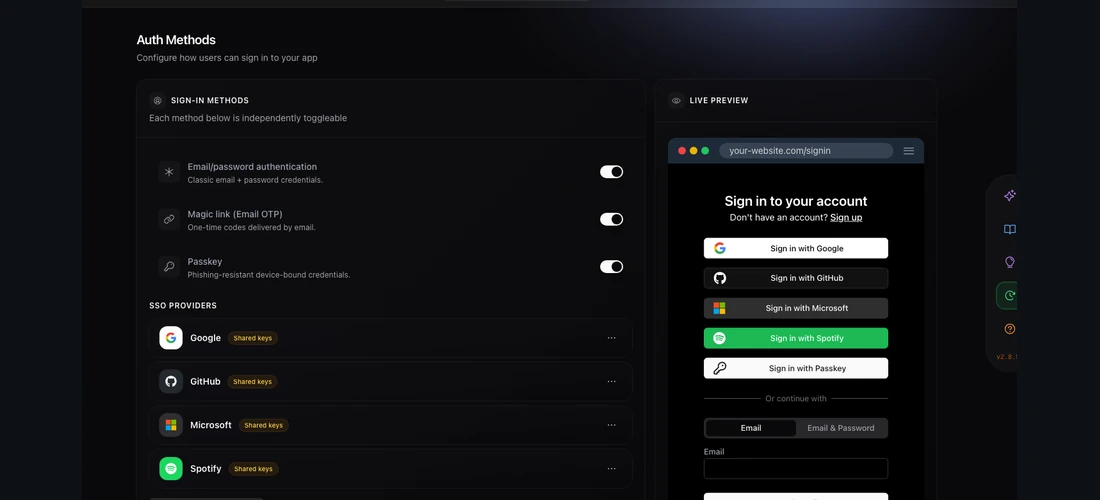
Capture screenshots from a running development site and prepare a pull request description with visual evidence.
Structure a pull request description around a visual summary, evidence, and merge danger.
Reduce unused Cargo features and prepare pull requests from staged Git changes.
Read and triage existing pull request review comments, or address them when requested.
Explain Git diffs or pull requests, affected components and potential change risks.
Review and maintain dsh-TUI, triage issues and pull requests, and navigate its user guide.
Work with user infrastructure, compare interface variants and prepare pull requests with visual evidence.
Pull request monitoring, HTML artifacts, Linear tickets and sandbox workspaces for Open SWE.
Write a self-contained HTML design document that explains a pull request and its before-and-after behavior.
Review diffs and pull requests, assess release readiness, and follow publishing steps.
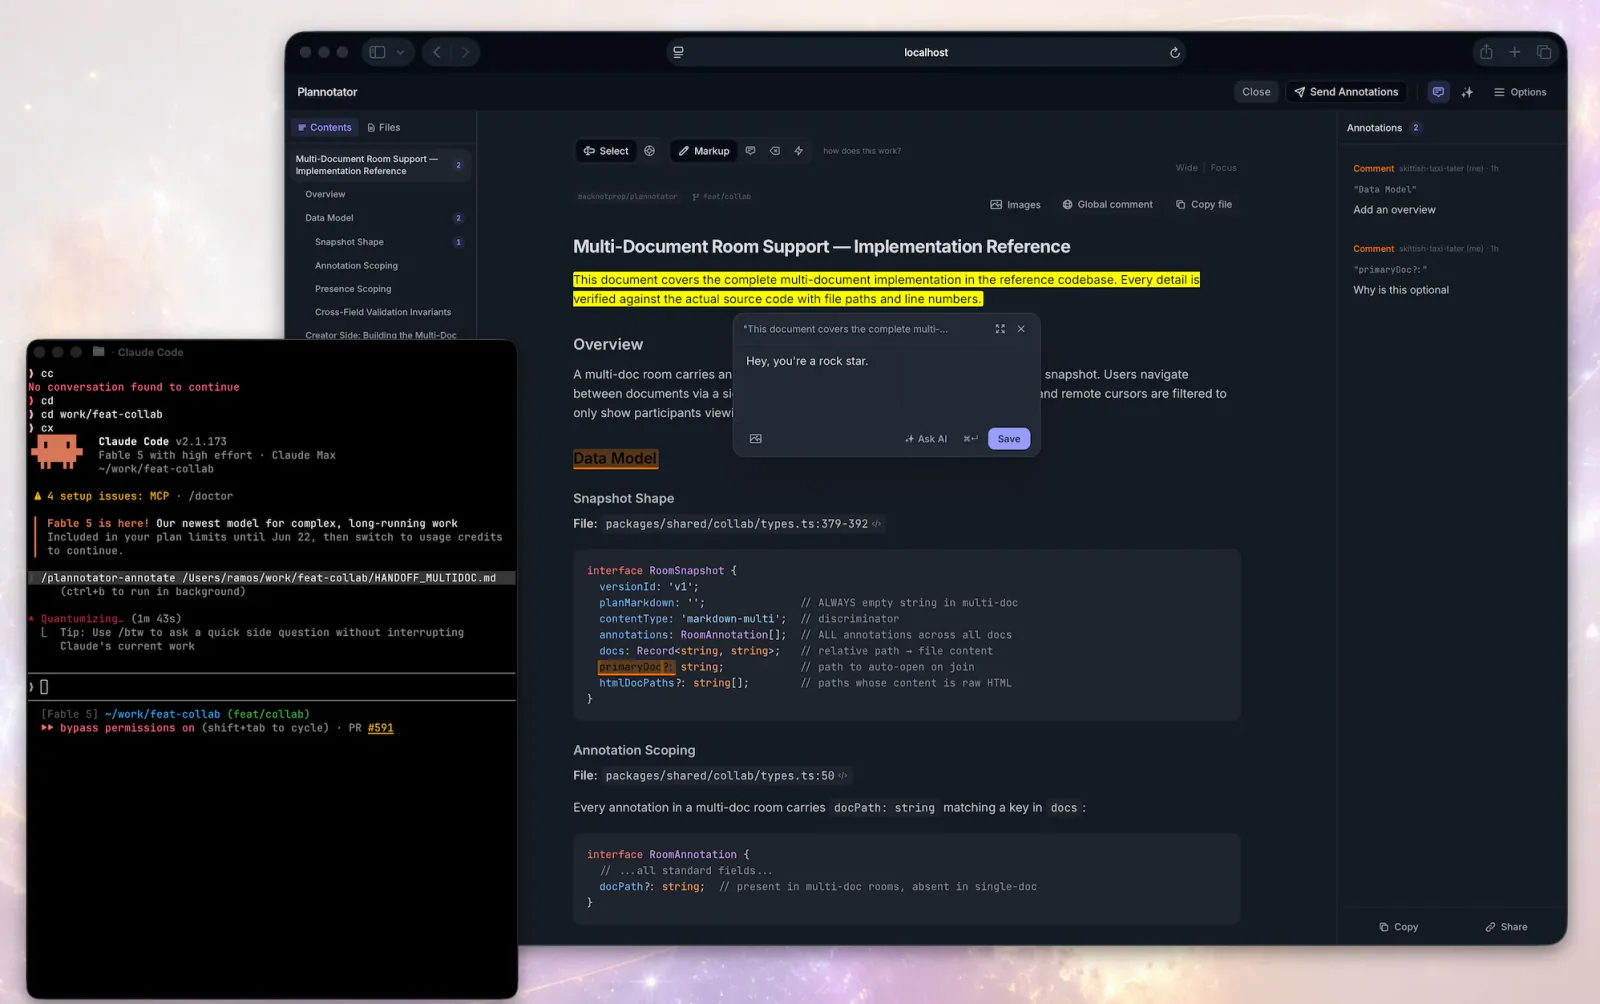
Open Plannotator's browser-based code review UI for the current worktree, another directory, or a pull request URL, then act on the feedback that comes back.

Review a branch, pull request or uncommitted change for introduced UI regressions.
Monitor a pull request, address actionable review feedback, and recheck CI until the PR meets its readiness criteria.
Add security scanning to CI/CD with Strix — GitHub Actions, GitLab CI, or any pipeline — so every pull request gets a diff-scoped AI pentest that blocks vulnerable code before it merges, with results as PR comments and SARIF uploaded to code scanning.
Uma pequena biblioteca feita com cuidado. Mais skills estão a caminho.