Free
Testing & security
Review Delta
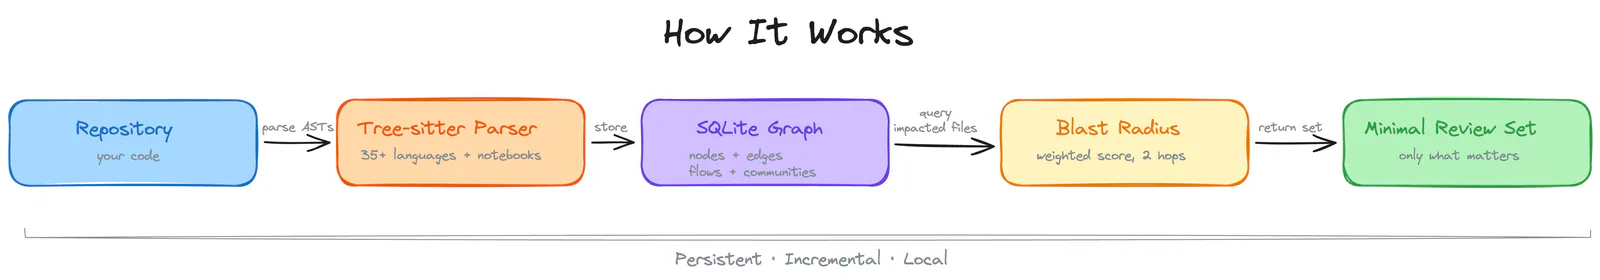
Review changes since the latest commit with incremental impact and blast radius analysis.
32.2KStars3KForks
Repository last pushed
tirth8205
Find skills for checking software behavior and examining code for defects and security issues.
56 skillsReview changes since the latest commit with incremental impact and blast radius analysis.
Review Renovate bot PRs that update GitHub Actions dependencies. Verifies supply chain integrity by checking pinned commit SHAs against upstream tagged releases, reviews changelogs for breaking changes, and confirms compatibility with existing workflow configurations.
Review code changes using detected modifications and their effects on dependent code.
Read and triage existing pull request review comments, or address them when requested.
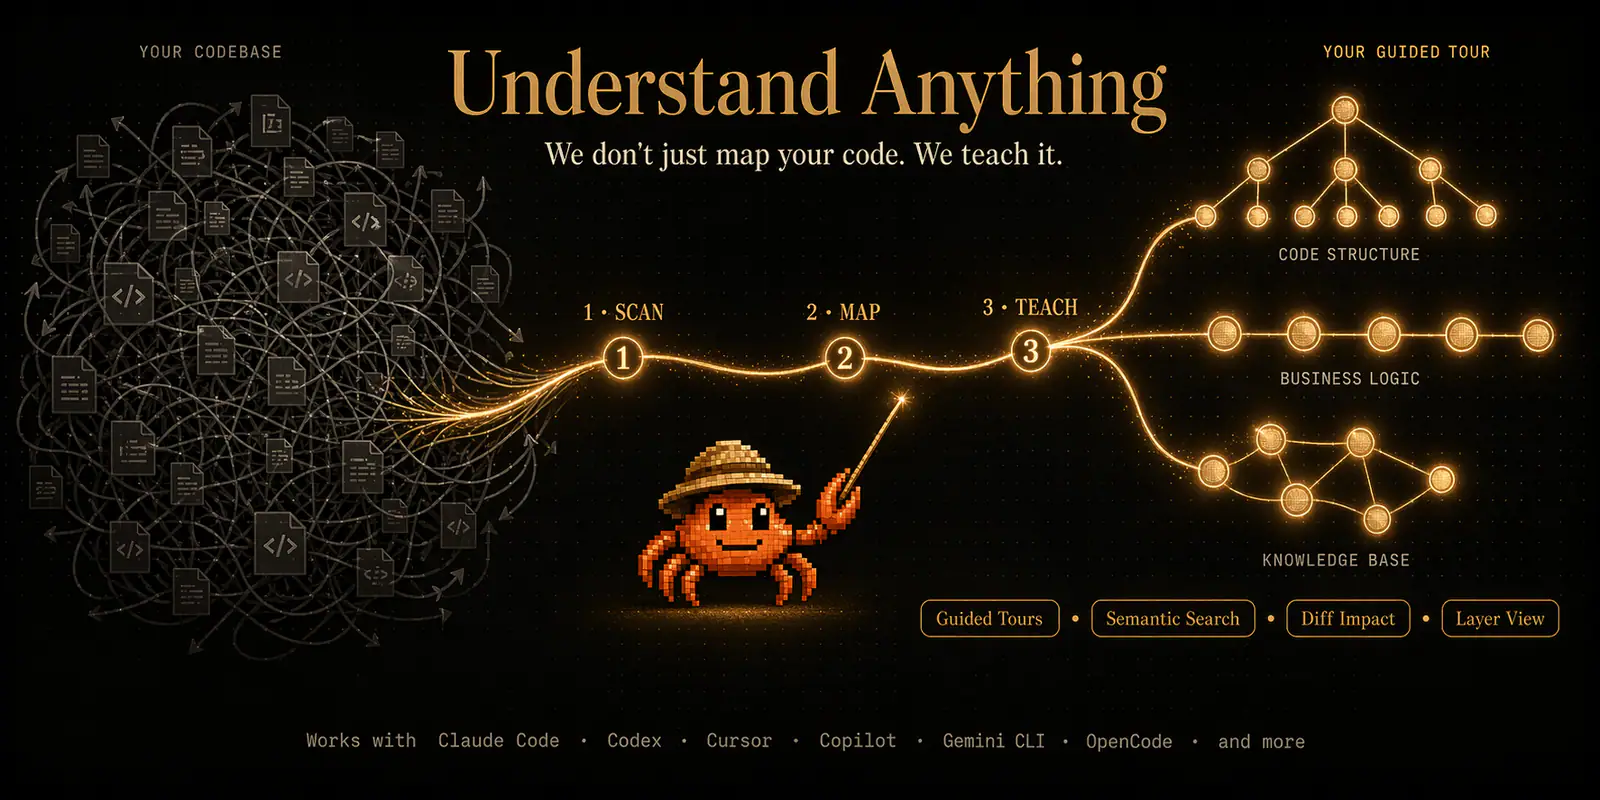
Explain Git diffs or pull requests, affected components and potential change risks.
Audit and update npm/Bun dependencies with supply chain integrity checks — verifies maintainers, publish age, tarball diffs, and provenance before bumping. Defers risky packages to ~/.supply-chain/notes/.
Apply task-oriented Rust guidance for ownership, error handling, async code, concurrency, API design, and code review.
Review or de-slop concrete changes in ccch1mneyyy/dsh-TUI at maintainer level: PR numbers or URLs, branches, commit ranges, patch files, staged or unstaged worktrees, and scoped repository-hygiene requests.
Review code for security, correctness, performance, maintainability and testing gaps.
Review changes for correctness, readability, architecture, security and performance with actionable findings.
Audit the repository or a broad subsystem for security, correctness, and maintainability risks.
Make the smallest complete change, with adjustable coding intensity and concise explanations.
Review diffs and pull requests, assess release readiness, and follow publishing steps.
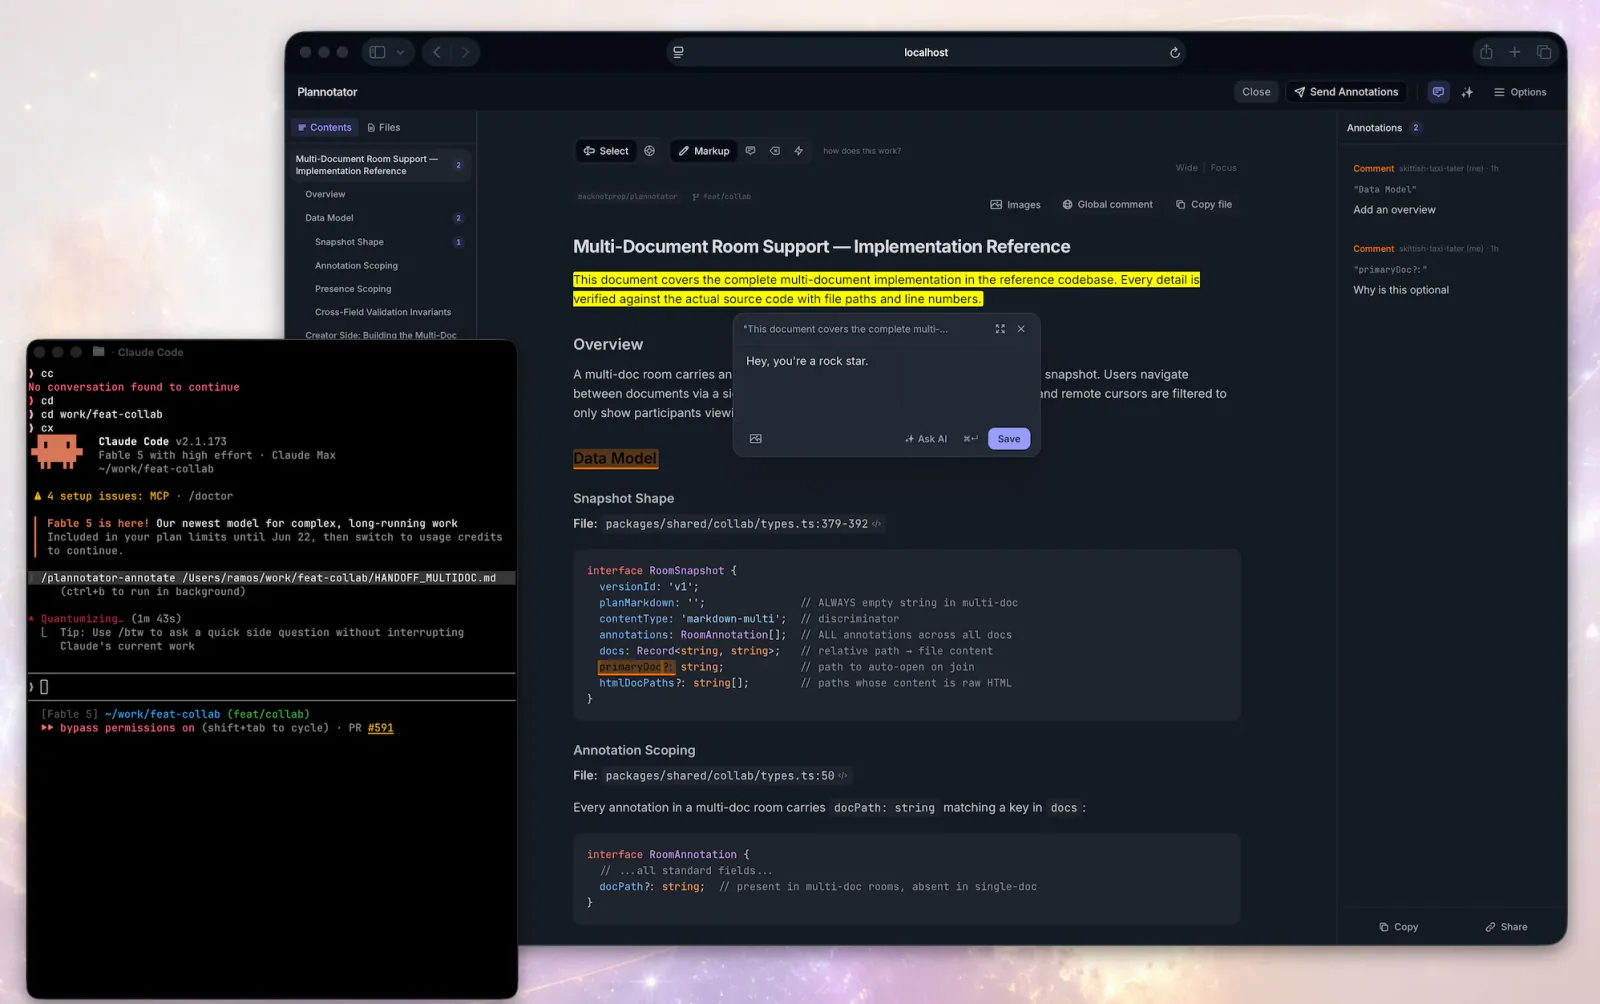
Open Plannotator's browser-based code review UI for the current worktree, another directory, or a pull request URL, then act on the feedback that comes back.
Audit a codebase, prioritize evidence-backed findings, and write implementation plans for another agent or developer.
Review pull requests and branch diffs with graph context and a structured impact report.
Cross-examine non-trivial engineering decisions using fresh-context adversarial review and explicit stop conditions.
Review a change and its connected code for correctness, safety, performance and unnecessary complexity.
Review a branch, pull request or uncommitted change for introduced UI regressions.
Monitor a pull request, address actionable review feedback, and recheck CI until the PR meets its readiness criteria.
Find security vulnerabilities in a codebase or repository with Strix — a white-box AI security review that reads your source, reasons about the actual data flow and authorization model, then exploits what it finds in a live sandbox so every reported issue has a working proof-of-concept instead of a noisy static-analysis alert.
Performs AI-powered code review on Git changes using the `ocr` CLI from alibaba/open-code-review.
Delegation mode for open-code-review (OCR).
Review Git changes with the OCR CLI, using either a configured model provider or the host agent for review reasoning.
Use Plannotator for plan and code review, artifact annotations, archived decisions and asynchronous feedback.
Choose a testing Skill for local web app flows, browser interactions or headless Godot test suites.
Compare code review skills for Git changes, graph context, focused findings and visual feedback. Choose a child workflow and give it a clear review boundary.
Compare five security Skills for source audits, secure implementation, Skill inspection, and authorized web and API penetration testing.
Find skills for checking software behavior and examining code for defects and security issues.