Free
Development & APIs
Debugging and Error Recovery
Find root causes through reproduction, localization, reduction, repair and regression protection.
110.9KStars11.6KForks
Repository last pushed
Addy Osmani, Federico Bartoli and Joan León
Find skills for checking software behavior and examining code for defects and security issues.
56 skillsFind root causes through reproduction, localization, reduction, repair and regression protection.
Inspect DOM, console, network and runtime behavior through Chrome DevTools MCP to investigate browser bugs.
Diagnose Vue runtime warnings, reactivity issues and SSR hydration problems.
Analyze failed GitHub Actions jobs, compare prior runs and identify the breaking change or flaky behavior.
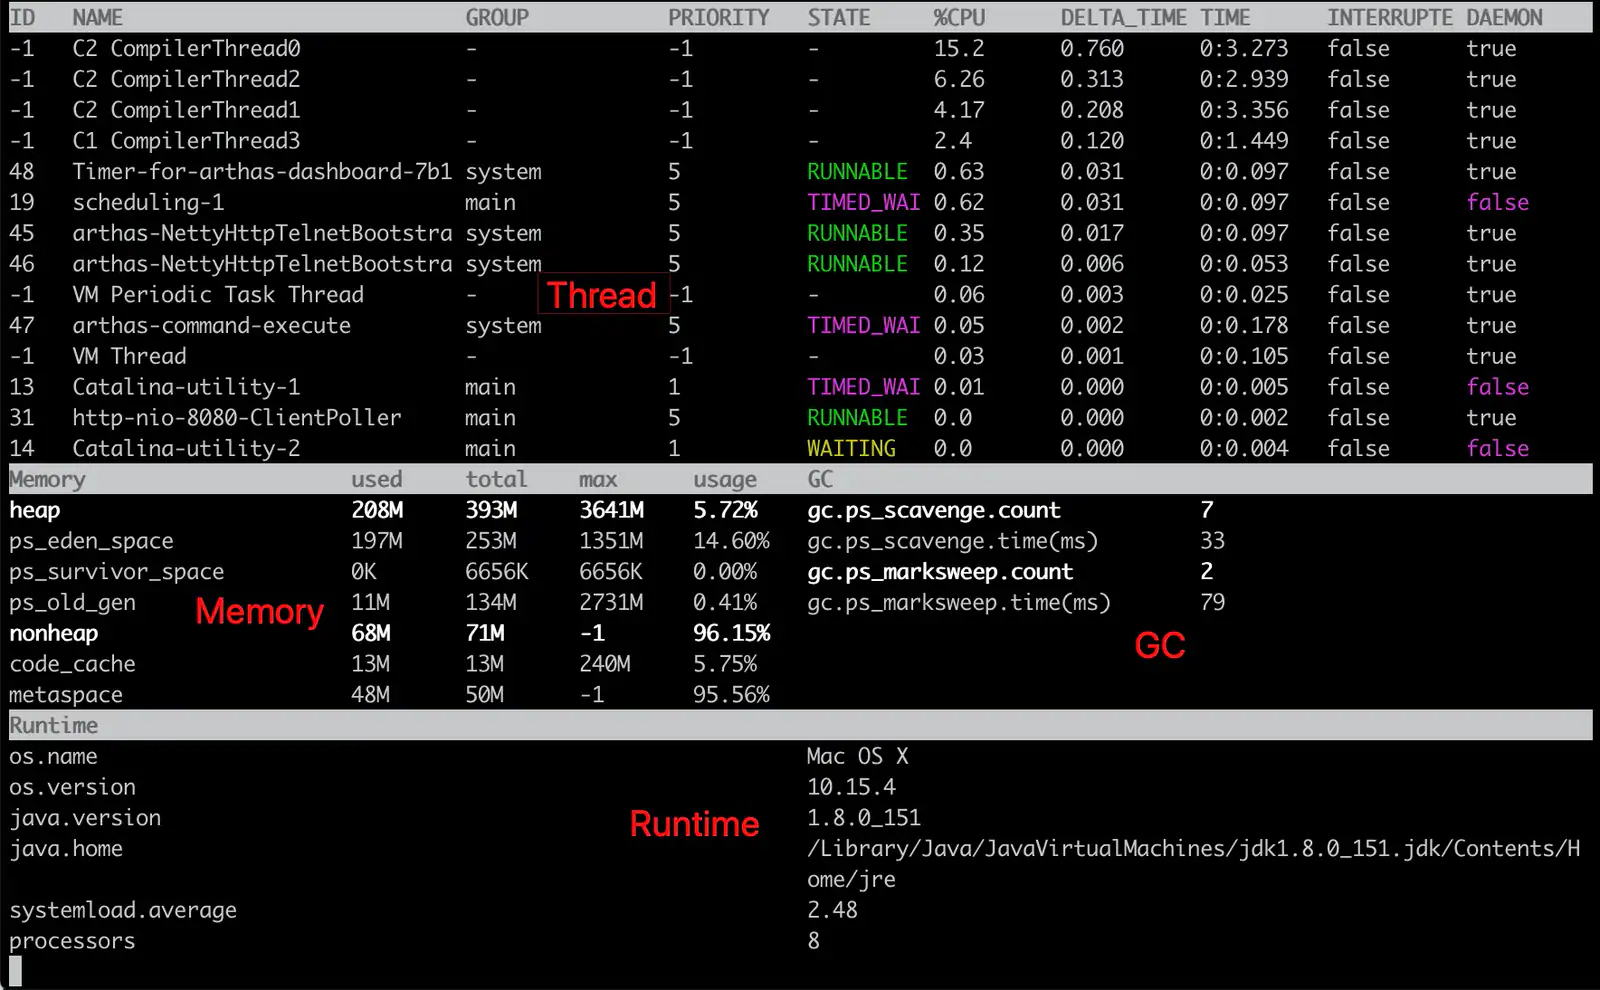
Investigate JVM CPU spikes with thread evidence, stack inspection, and bounded method tracing.
Investigate the root cause of errors, crashes, and regressions before proposing a fix.
Inspect and debug Honcho workspaces via the `honcho` CLI.
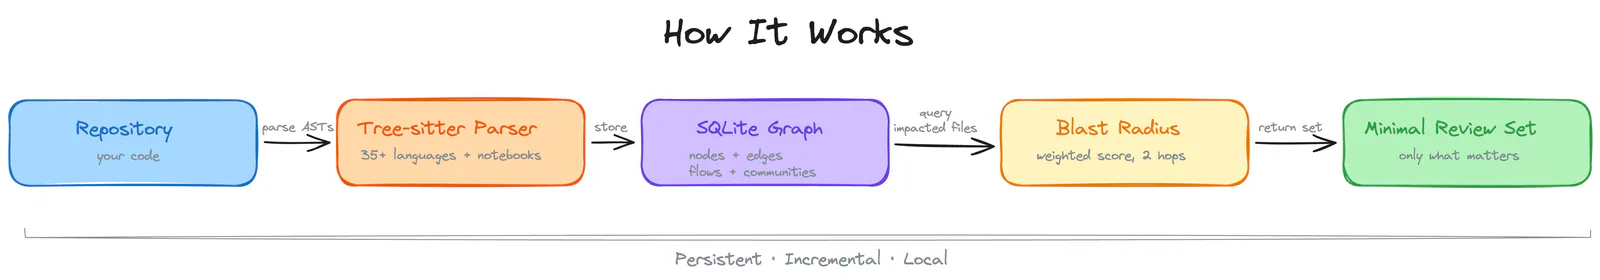
Use a repository knowledge graph to locate relevant code and investigate reported issues.
Reproduce terminal, process and agent issues in a disposable named Herdr session while preserving the main session.
Retrieve EagleEye trace IDs with Arthas to connect request execution with application logs.
Turn a reported defect into an actionable bug report or issue draft.
Monitor a pull request until CI succeeds, investigate failures and retry only confirmed flaky workflow jobs.
Inspect Spring application contexts, bean definitions, and configuration sources with Arthas.
Investigate Node.js internals, V8, libuv, native addons and build failures.
Run the Open SWE dashboard locally against real GitHub data using an authenticated gh CLI.
Fix security vulnerabilities found by a Strix pentest (open-source CLI or app.strix.ai cloud) — triage by severity, patch the root cause rather than the symptom, and re-run Strix to prove each fix actually closes the exploit.
Diagnose WxJava credentials, signatures, certificates, callbacks and multi-account configuration.
Automatically fix broken OpenCLI adapters when commands fail.
Choose a testing Skill for local web app flows, browser interactions or headless Godot test suites.
Compare code review skills for Git changes, graph context, focused findings and visual feedback. Choose a child workflow and give it a clear review boundary.
Compare five security Skills for source audits, secure implementation, Skill inspection, and authorized web and API penetration testing.
Find skills for checking software behavior and examining code for defects and security issues.